
Services / Security Engineering
Security Engineering
Security controls,
built to keep up.
Design, implement and run the controls that keep your environment secure as it changes.
- Design & implementation
- Cloud & infrastructure engineering
- EDR / MDR
- SIEM
- IAM
- Email gateway
- Secure file transfer
Security controls we deploy, connected around the Insyghts shield
- IdP — Identity provider
- EDR — Endpoint detection & response
- PAM — Privileged access management
- Cloud — Cloud security
- SIEM — Log monitoring & correlation
- MFT — Secure file transfer
- IAM — Identity & access management
- DLP — Data loss prevention
- MFA — Hardware security keys
- PKI — Certificate authority
- Email — Email security gateway
- Segmentation — Network segmentation
Technologies and partners


The engineering gap
Installed isn’t the same as working.
Most security tools are bought for good reasons. Many are then left on default settings, half-deployed or unwatched once the project team moves on.
- Tool purchased
- Not tuned
Running on defaults
Features you paid for stay switched off, and alerts go unread.
- Installed
- Effective
- Logs collected
- Not correlated
Data without insight
Logs sit in separate systems, so no one sees the full picture.
- Collected
- Correlated
- Access granted
- Not reviewed
Accounts that never expire
Leavers’ accounts, shared admin logins and missing MFA quietly widen the attack surface.
- Granted
- Controlled
Security engineering keeps your controls configured, connected and current.
What we do
Controls across your environment, built to work together.
From identity to the cloud, we design and implement each control, then connect it to the rest.
In practice
What we’ve implemented, and still run.
Engagements we’ve delivered, from a single control to a managed stack. Select one to see the challenge, what we built and how we run it.
- Client engagement
- Challenge
- What we built
- How we run it
Financial services
Implemented
Migrating email security to Proofpoint SaaS
- Proofpoint SaaS
- Email gateway
- Rule migration
An on-premises email security gateway was due for replacement, and the business relied on the filtering rules built up in it over the years.
Moved the organisation to a Proofpoint SaaS instance, migrated every rule from the old system and cut mail flow over for more than 3,000 users.
We provided the project manager and deployment engineers, from planning and testing through cutover and handover.
More than 3,000 users moved to Proofpoint with zero downtime, and every rule carried across.
Utilities
Implemented
A new certificate authority and hardware MFA
- Certificate authority (PKI)
- YubiKey
- Hardware MFA
Sign-ins relied on passwords, and there was no internal certificate authority to issue trusted certificates to users, devices and systems.
Designed and built the complete certificate authority (CA) infrastructure for issuing, renewing and revoking certificates, then rolled out YubiKey hardware keys for multi-factor sign-in.
Handed over with documentation and runbooks for issuing certificates and replacing lost keys.
Sign-ins are protected by hardware keys, backed by the organisation’s own trusted CA.
Insurance
Implemented & managed
Endpoint protection, watched 24/7
- TrendAI EDR
- MDR
- 24/7 SOC
Several antivirus products across offices, no central view and nobody watching alerts after hours.
Rolled out TrendAI endpoint detection and response, removed the legacy agents and tuned detection policies for staff devices and servers.
Alerts go to our 24/7 security monitoring, with monthly tuning and health checks.
One console covers every endpoint, and alerts are followed up around the clock.
Manufacturing
Implemented
Splitting a flat network into zones
- Firewall
- Segmentation
- Jump hosts
Office laptops, servers and production systems shared one flat network, so one infected device could reach everything.
Designed user, server, management, production and guest zones, with firewall rules and jump hosts for admin access, rolled out in stages.
The client’s team runs the network day to day, and we review rules and changes each quarter.
Critical systems can only be reached from approved zones and hosts.
Systems integrator
Partner delivery
White-label delivery for an SI’s customer
- EDR
- SIEM
- Email gateway
An integrator had won a security project but didn’t have engineers free to deliver it.
Our team designed and deployed the controls under the integrator’s brand, following their project method and documentation templates.
We provide second-line support behind the integrator’s service desk.
The integrator delivered on time without hiring, and kept the customer relationship.
How it connects
Every control feeds the bigger picture.
We engineer controls to share their data, so your SIEM and our 24/7 security monitoring see the whole environment, not isolated tools. Select a control to see what it contributes.
- Control
- Sends to the SIEM
- Platforms we work with
Correlate
SIEM
Syslog and events from every control, turned into alerts.
Ways to work with us
Engineering, the way it fits your team.
Start with a single project, hand us the day-to-day, or bring us in behind your own brand.
01 · Project
Project delivery
Scoped design, deployment and handover, with documentation your team can run.
Best forNew controls, migrations and upgrades
02 · Managed
Managed engineering
We keep your controls tuned, patched and reviewed after go-live.
Best forTeams without spare engineering time
03 · Partner
Partner & white-label delivery
Design, deployment and support for your customers, under your brand or ours.
Best forSystems integrators and vendors
04 · Augment
Team augmentation
Engineers from our Singapore team, working inside yours for a set period.
Best forPeaks, projects and cover
How it works
From design to day-to-day running.
Engineering doesn’t stop at go-live.
Environments change every week. Each review feeds the next change, so your controls keep matching how you actually work.
What we do
- Design and document the architecture
- Deploy, configure and test each control
- Tune, patch and review, if you choose managed engineering
What you own
- Approve designs and change windows
- Provide access and system owners
- Decide which risks to accept
Who does the work
Built by our Singapore team.
Singapore-based
Delivered by our Singapore team. No foreign team augmentation.
Held by our team
Partner certifications

Connected and continuous
Controls need direction, and eyes on them.
Engineering builds the controls. Our other services set their direction and watch them around the clock.
01
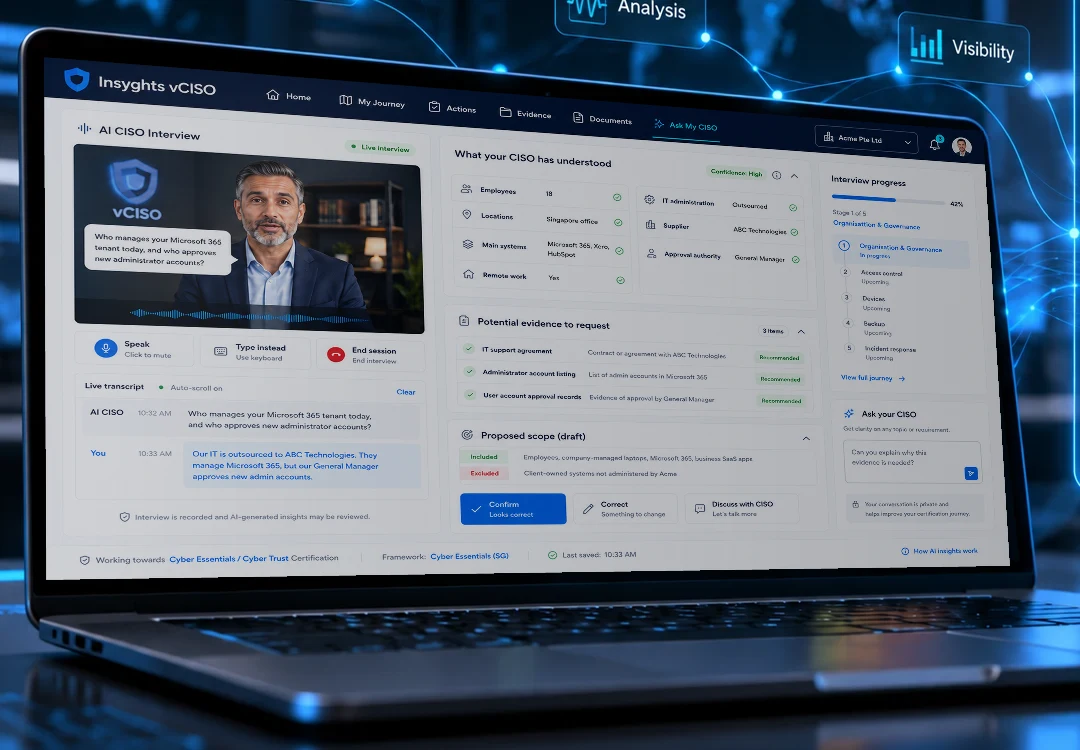
Governance
Turn security obligations into clear priorities, practical policies and a plan your team can maintain.
02
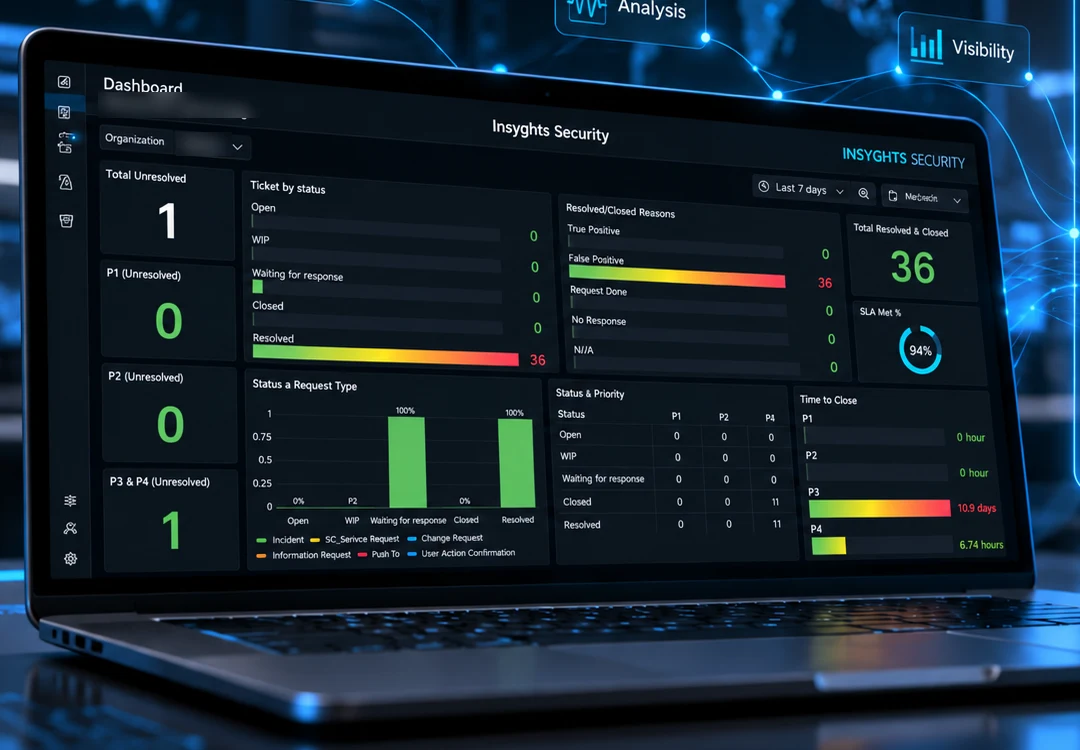
Security Operations
Monitor, detect and follow through, so alerts turn into action, around the clock.
Resources
See what an attacker would see.
Start with a quick look at what’s exposed.
Stage 01 · Just starting
Domain scan
Understand your exposure.
Stage 04 · Mature, want to improve
Attack surface assessment
Find and close gaps.
Coming soon
What do you need to build or fix next?
Tell us about your environment and the controls you’re planning, and we’ll suggest a starting point.
- 16 Jalan Kilang Timor, #04-06 Redhill Forum, S159308
- [email protected]
- +65 8749 4825