
Services / Governance
Governance
Security obligations,
turned into a plan.
Turn security obligations into clear priorities, practical policies and a plan your team can maintain.
- CISO-as-a-Service
- Risk assessment
- Certification readiness
- CSA Cyber Trust & Cyber Essentials
- ISO 27001
The governance gap
A policy on paper isn’t a practice.
Many organisations have the documents. Fewer have clear owners, current priorities and evidence ready when an assessor asks.
- Policy approved
- Not embedded
Written once, then shelved
Policies exist, but day-to-day work doesn’t follow them.
- Paper
- Practice
- Risks known
- Not prioritised
Everything feels urgent
Without a risk-based plan, effort goes to what’s loudest, not what matters.
- Known
- Treated
- Certification target
- No owner
No one leads security
Deadlines approach without anyone accountable for readiness.
- Target
- Ready
Governance should give your team direction, not more paperwork.
What we do
From first assessment to certification readiness.
70%
Up to · co-funding
CSA-listed CISO-as-a-Service consultant
Eligible SMEs can receive up to 70% co-funding for a cybersecurity health plan and VAPT under CSA’s SG Cyber Safe Programme.
Subject to CSA and IMDA eligibility and approval.
Frameworks
Prepare for the standard you need.
Start where your customers, regulators or tenders require, and build toward the next level.
- Baseline
Cyber Essentials - Risk-based
Cyber Trust - Management system
ISO/IEC 27001
How it works
A plan your team can maintain.
Governance is a cycle, not a project.
Each round of assessment, planning and audit feeds the next, so your programme keeps pace with new risks and requirements.
What we do
- Lead the assessment and plan
- Draft policies and the management system
- Guide you through audit preparation
What you own
- Approve policies and decisions
- Supply evidence and maintain controls
- Certification is decided by the certifying body
Connected and continuous
Policies need to be put into practice.
Governance sets direction. Our other services keep it working.
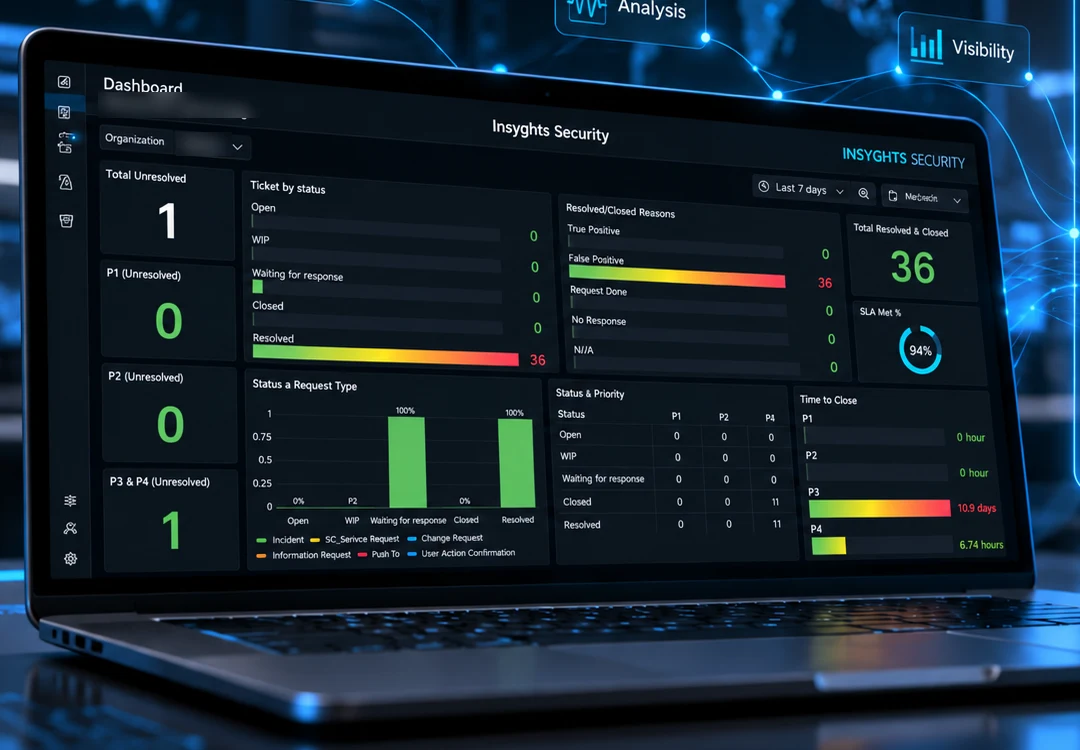
Security Operations
Monitor, detect and follow through, so alerts turn into action, around the clock.
Security Engineering
Design, implement and run the controls that keep your environment secure as it changes.
Resources
Tools to check where you stand.
Start with a quick look at your exposure or readiness.
Stage 01 · Just starting
Domain scan
Understand your exposure.
Coming soon
Stage 02 · Getting compliant
Cyber Essentials readiness assessment
See how close you are to certification.
Coming soon
Stage 04 · Mature, want to improve
Attack surface assessment
Find and close gaps.
Coming soon
Where does your governance need to go next?
Tell us your target framework or challenge, and we’ll suggest a starting point.